رؤى / تقرير بحثي
ابنِ ذاكرة للقرارات المؤثرة
تتبّع الأدلة والصلاحيات والنتائج في القرارات المدعومة بالذكاء الاصطناعي
توليف للمصادر الأولية وتحليل mayden. المنهج والحدود موضحان.
الملخص التنفيذي
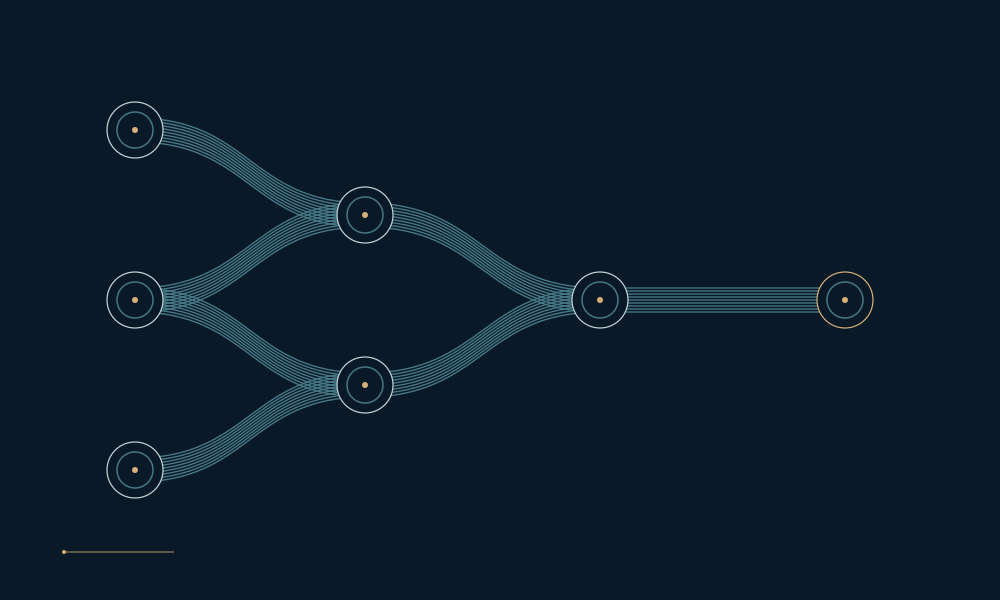
- اربط كل قرار بمصادره وإعدادات النظام والصلاحيات والنتيجة المرصودة.
- افصل بين أصل المعلومة وسلامة السجل وصحة الادعاء.
- اختبر قدرة شخص مستقل على إعادة بناء القرار مع تقليل البيانات المحتفظ بها.
اقرأ التقرير الكامل بالإنجليزية
يتوفر الملخص التنفيذي بالعربية. يتضمن التقرير الإنجليزي التحليل الكامل والرسوم التوضيحية والأسئلة القيادية والمراجع.
قراءة التقرير بالإنجليزيةتنزيل التقريرمنهج البحث وحدوده
كيفية قراءة هذا البحث
تفاصيل المنهج والمراجع أدناه باللغة الإنجليزية.
- Approach
- Narrative synthesis of eight primary research and technical specifications accessed 10 October 2026, combined with a proposed mayden receipt architecture.
- Source selection
- Provenance models, explanation faithfulness, software provenance, security logging, transparency logs, content credentials and dataset documentation.
- Limitations
- No claim of legal sufficiency, forensic certification or perfect replay. RFC 9162 is an experimental certificate protocol; C2PA concerns content credentials. Their application to business decisions is an explicitly labeled analogy.
المراجع / 8 مصادر
الأدلة التي يستند إليها التحليل
- [1]PROV-DM: The PROV Data Model ↗
W3C · 2013-04-30
Technical recommendation · Overview; entities, activities and agents
A provenance data model for describing entities, activities and agents; recording these relationships does not prove that a decision or its inputs are correct.
- [2]Language Models Don't Always Say What They Think: Unfaithful Explanations in Chain-of-Thought Prompting ↗
Turpin et al.; NeurIPS · 2023-12-09
Peer-reviewed research · Abstract
Experiments on specified historical language models; show potential unfaithfulness of generated explanations, not that all explanations are always misleading.
- [3]SLSA v1.2: Build Provenance ↗
SLSA project · Version 1.2; accessed 2026-10-10
Technical specification · Schema; buildDefinition and runDetails
Version 1.2 concerns software build provenance. The decision-lineage analogy is mayden interpretation; SLSA does not certify business legitimacy or semantic truth.
- [4]SP 800-92: Guide to Computer Security Log Management ↗
NIST · 2006-09
Technical guidance · Abstract
Foundational log-management guidance published in 2006; not an AI-specific standard or evidence that logging alone assures decisions.
- [5]RFC 9162: Certificate Transparency Version 2.0 ↗
IETF · 2021-12
Experimental RFC · Sections1 and2.1
Experimental RFC for certificate transparency, not a general decision-audit standard. Inclusion and consistency proofs do not establish correctness of logged content.
- [6]Content Credentials: C2PA Technical Specification 2.2 ↗
C2PA · Version2.2; accessed 2026-10-10
Versioned technical specification; not a latest-version claim · Introduction; claims and assertions
Version 2.2 is deliberately pinned. Cryptographic provenance supports verification of signed assertions and history, not the factual truth of the content.
- [7]Datasheets for Datasets ↗
Gebru et al.; CACM · 2021-12-01
Peer-reviewed research · Abstract
Dataset-documentation proposal; a completed datasheet neither establishes representativeness nor guarantees data quality or lawful use.
- [8]AI Act, Article 12: Record-keeping ↗
European Commission AI Act Service Desk · Consolidated text as at 2026-07-27; accessed 2026-10-10
Official legal text presentation · Article 12(1)–(2); scope heading
Does not impose universal logging duties on every AI application or provide case-specific legal advice.